The EU compliance cliff is 72 days away. Is your team ready for what the AI Act and the CRA will actually require?
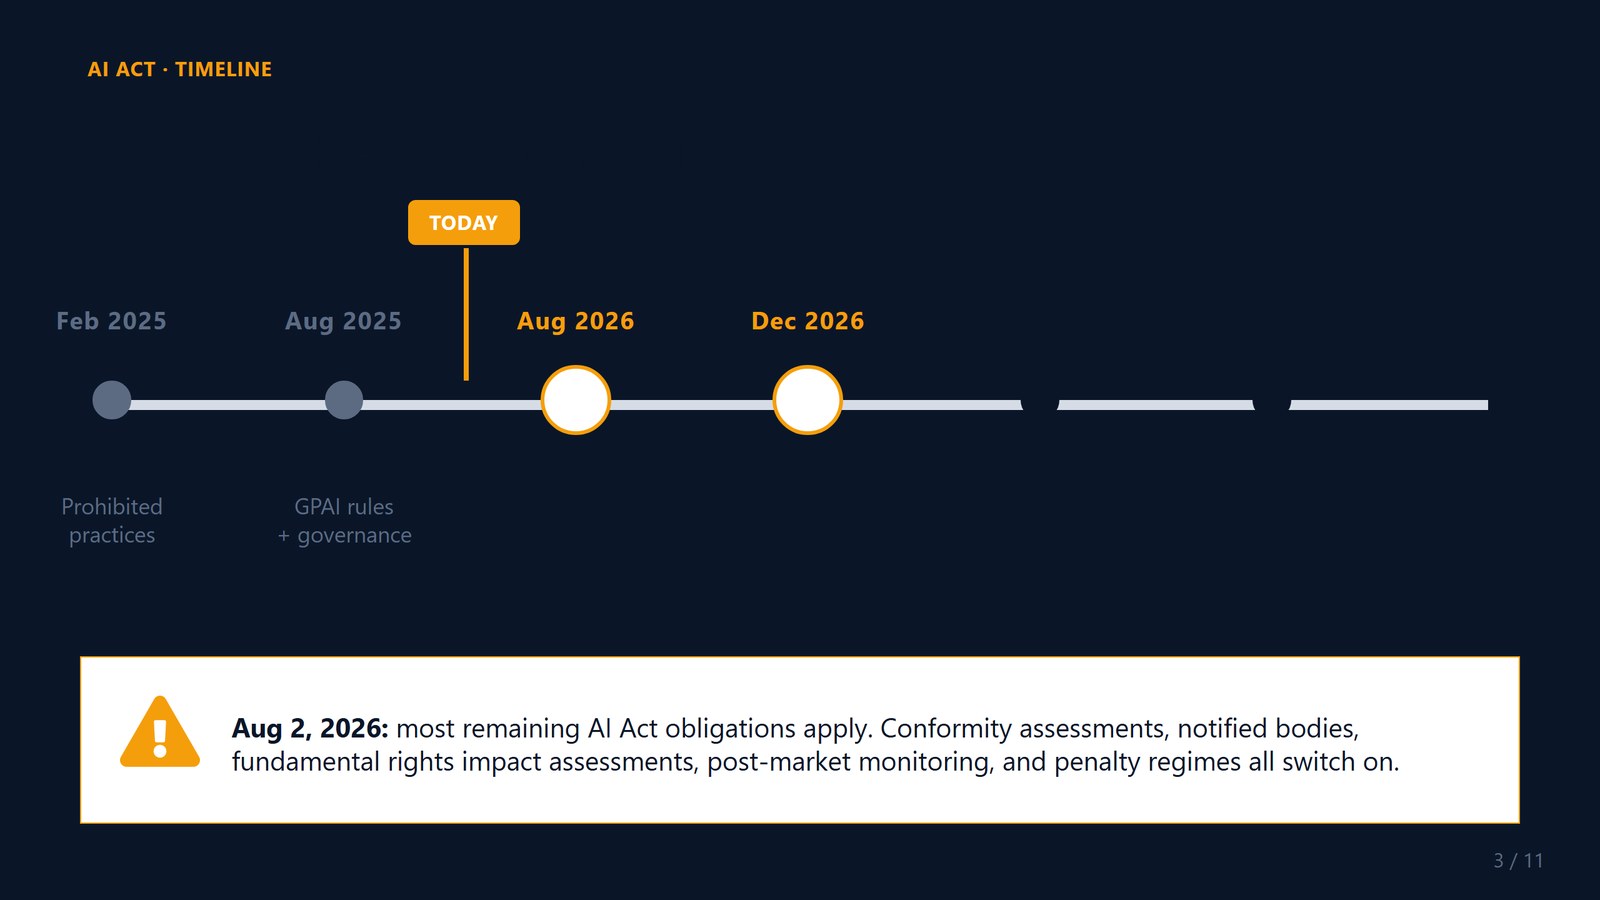
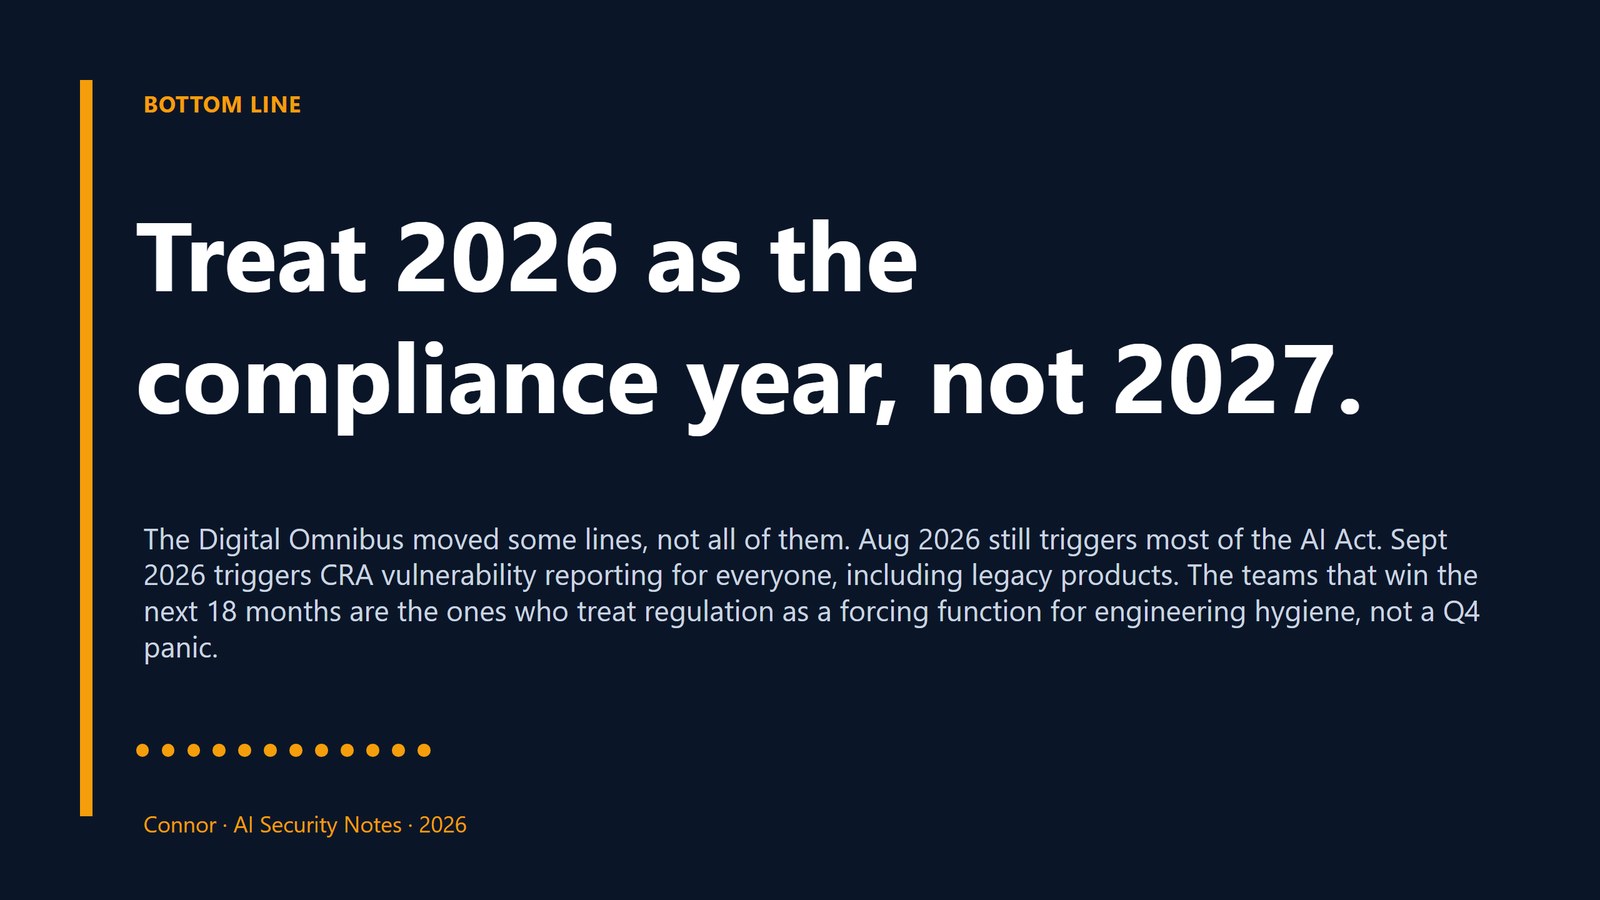
Three 2026 deadlines define the rest of the year for anyone shipping AI into the EU:
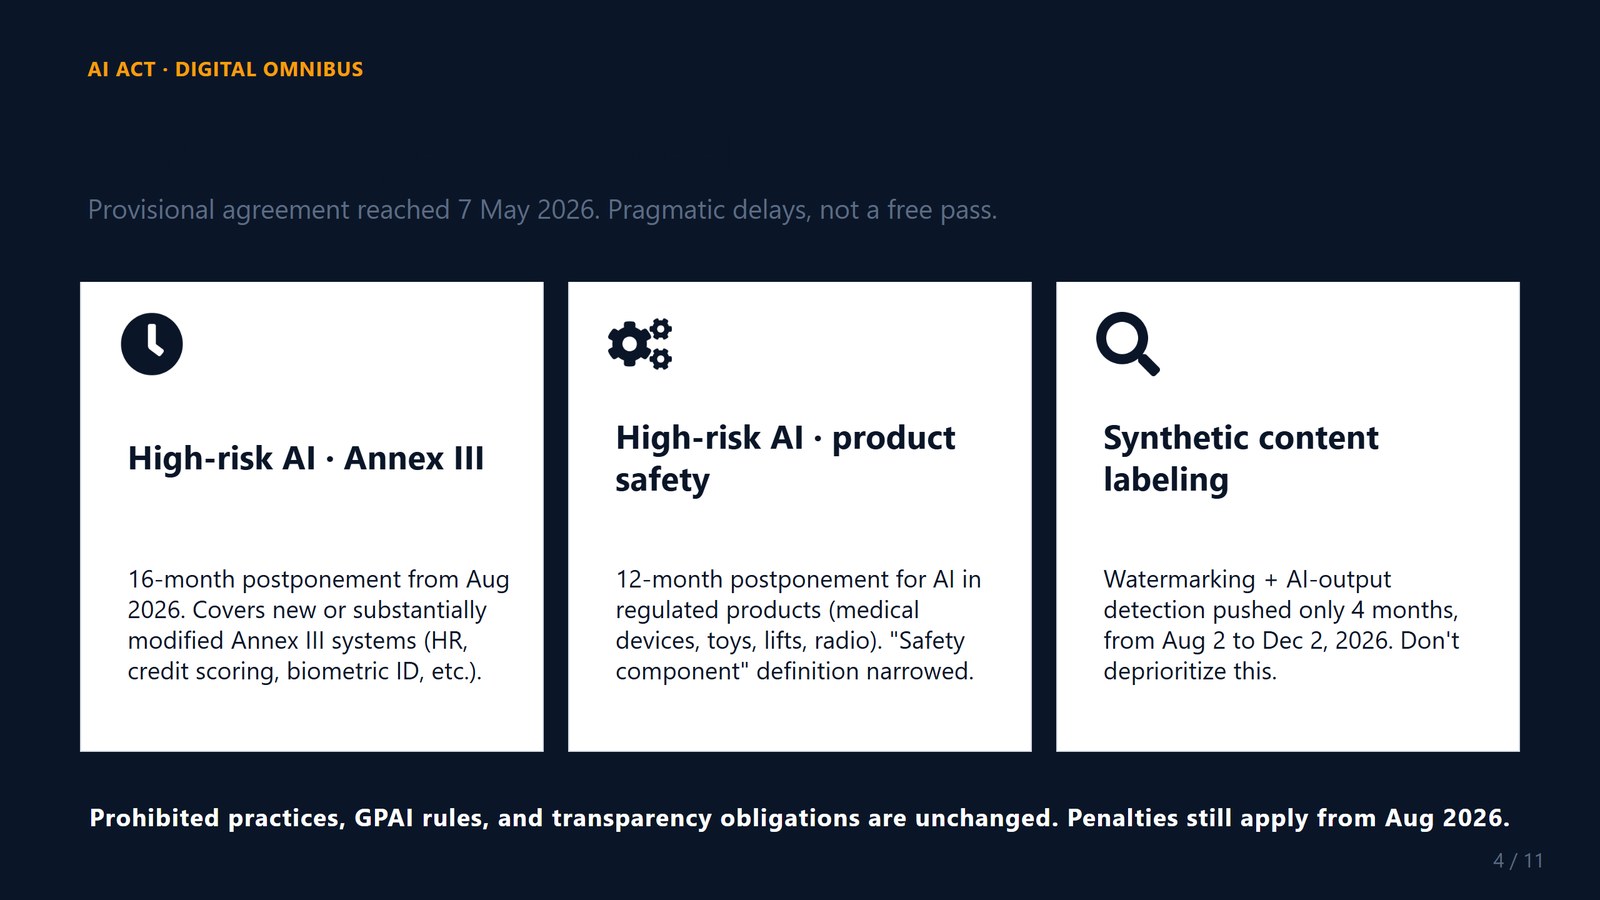
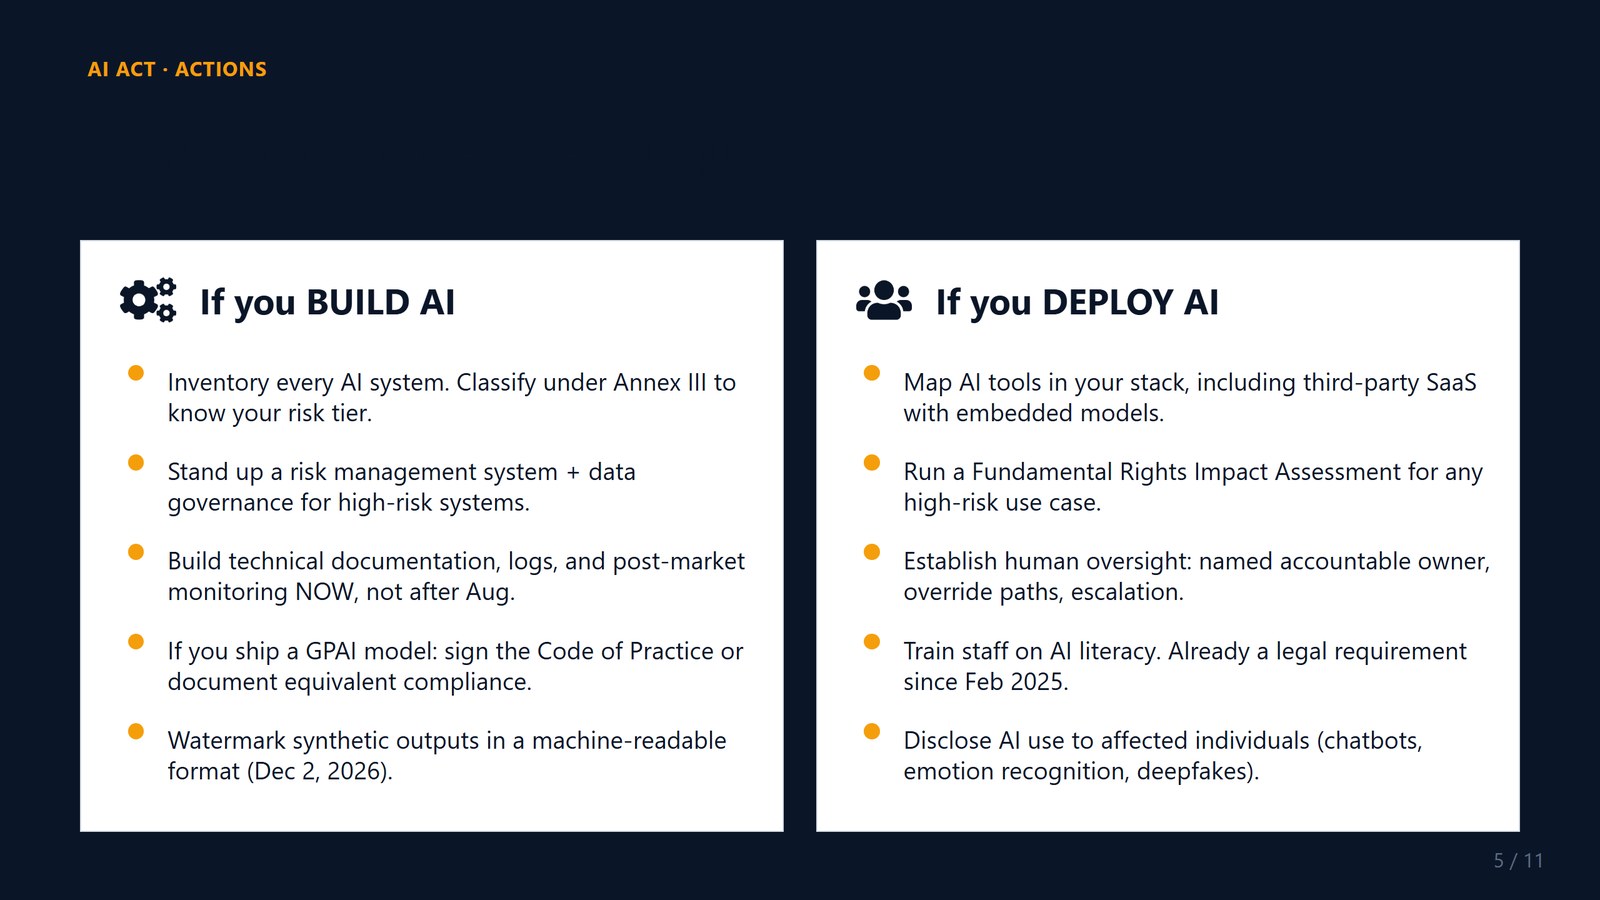
- Aug 2, 2026 — most of the AI Act applies. Conformity assessments, post-market monitoring, fundamental rights impact assessments, transparency obligations, GPAI rules.
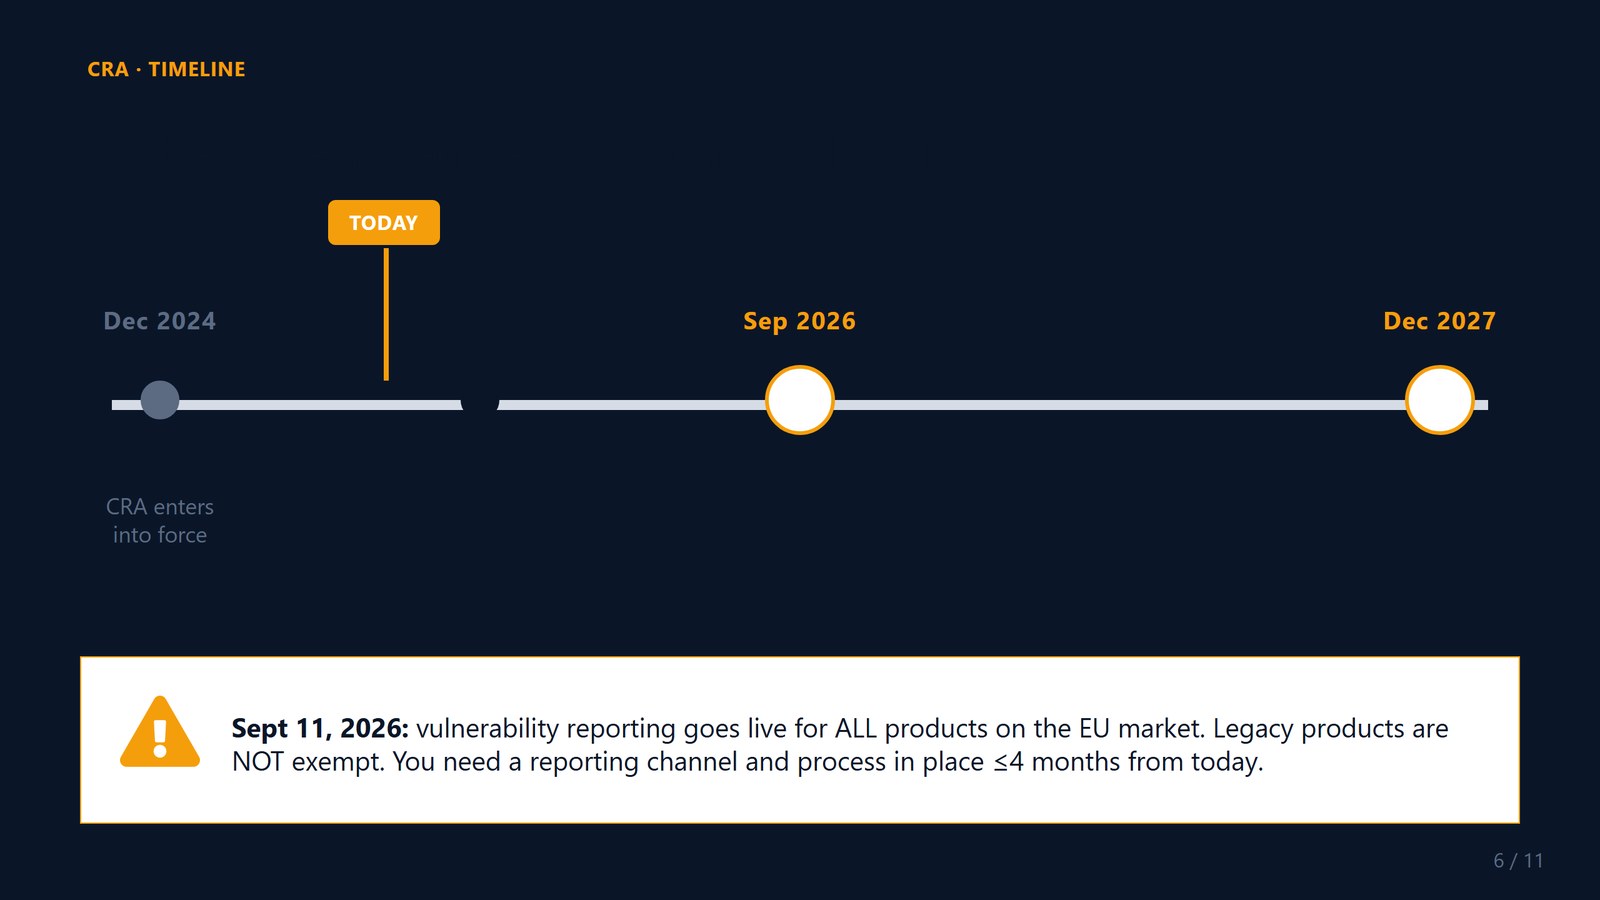
- Sept 11, 2026 — CRA vulnerability reporting goes live. Every product with digital elements on the EU market, legacy products included.
- Dec 2, 2026 — synthetic content watermarking under the AI Act.
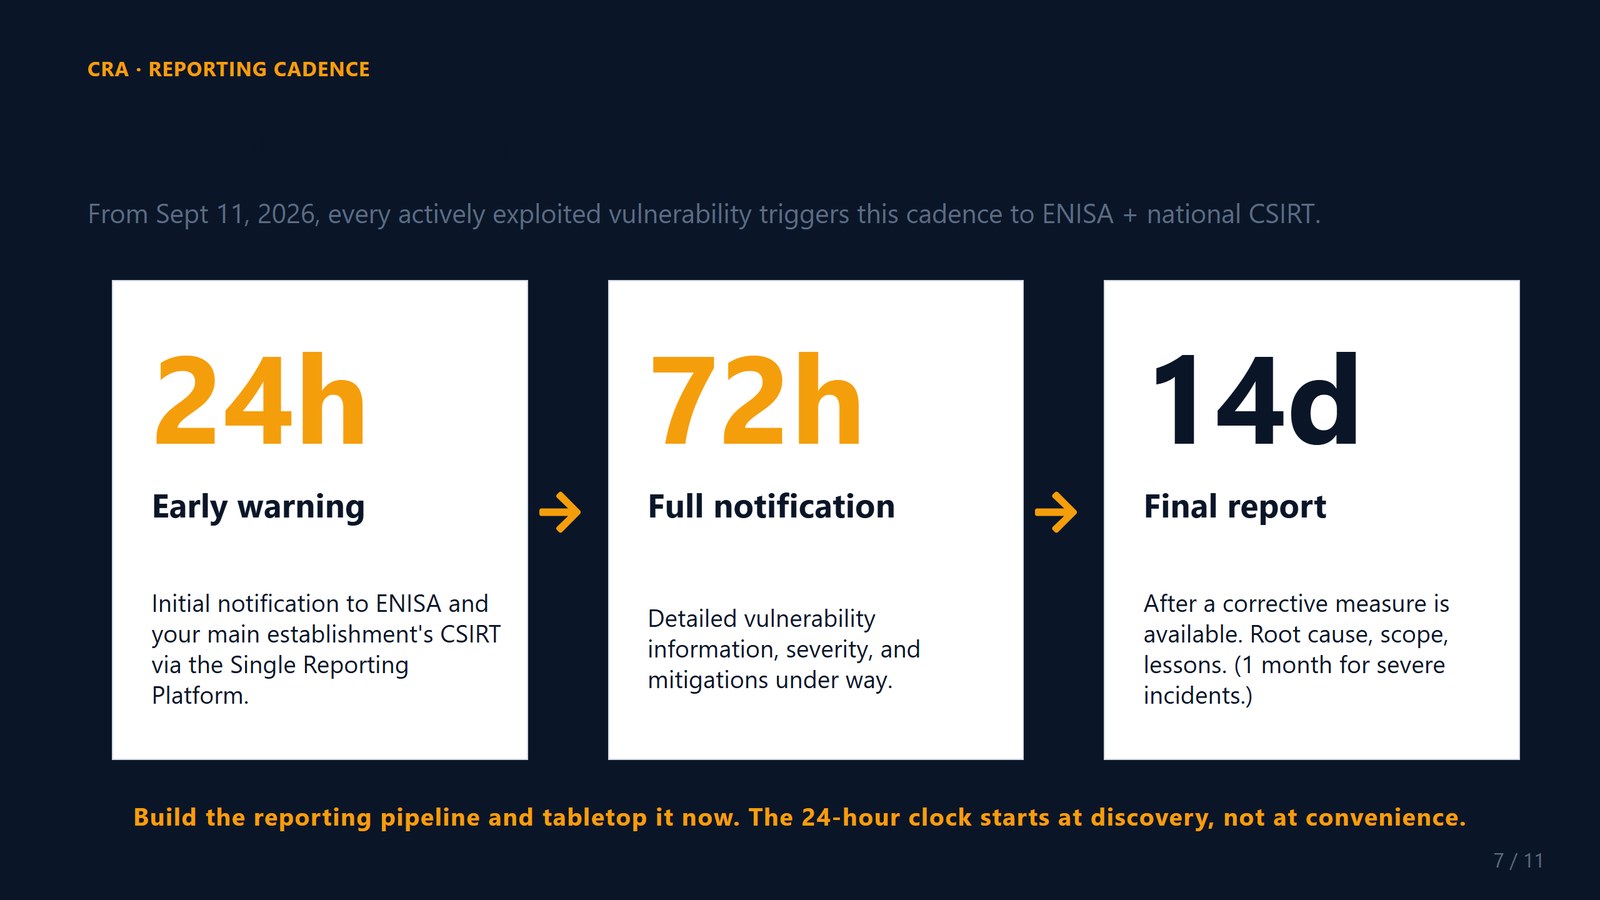
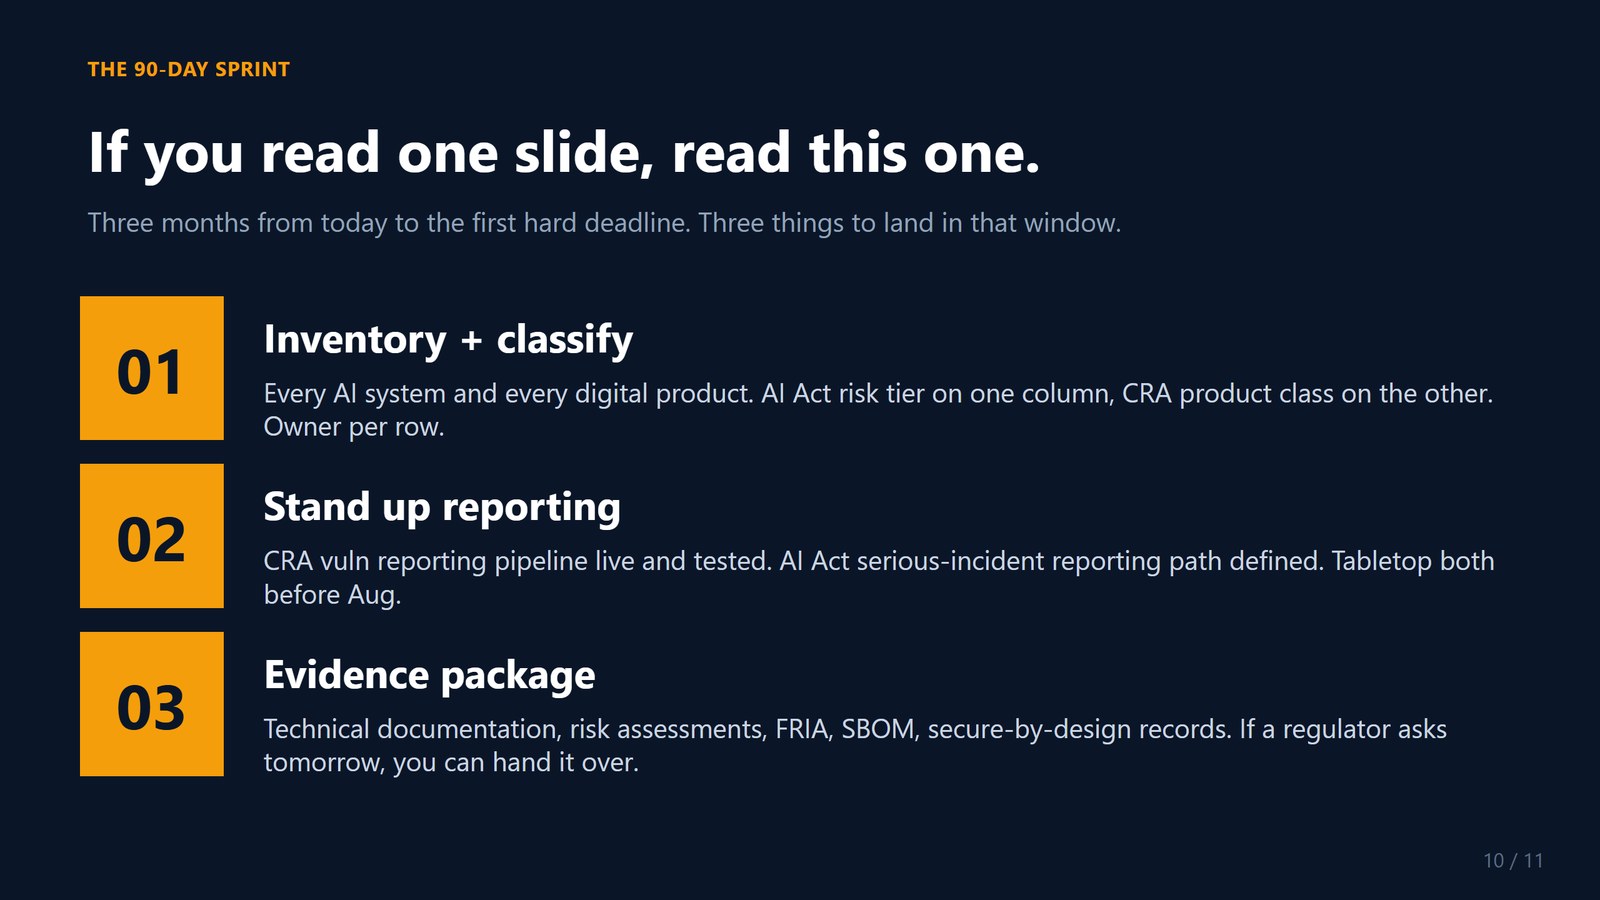
The CRA reporting cadence is the part most security teams haven’t internalised. 24h early warning to ENISA and your national CSIRT. 72h full notification. 14d final report. The clock starts at discovery, not at convenience, and most teams don’t have a tested 24h pipeline yet.
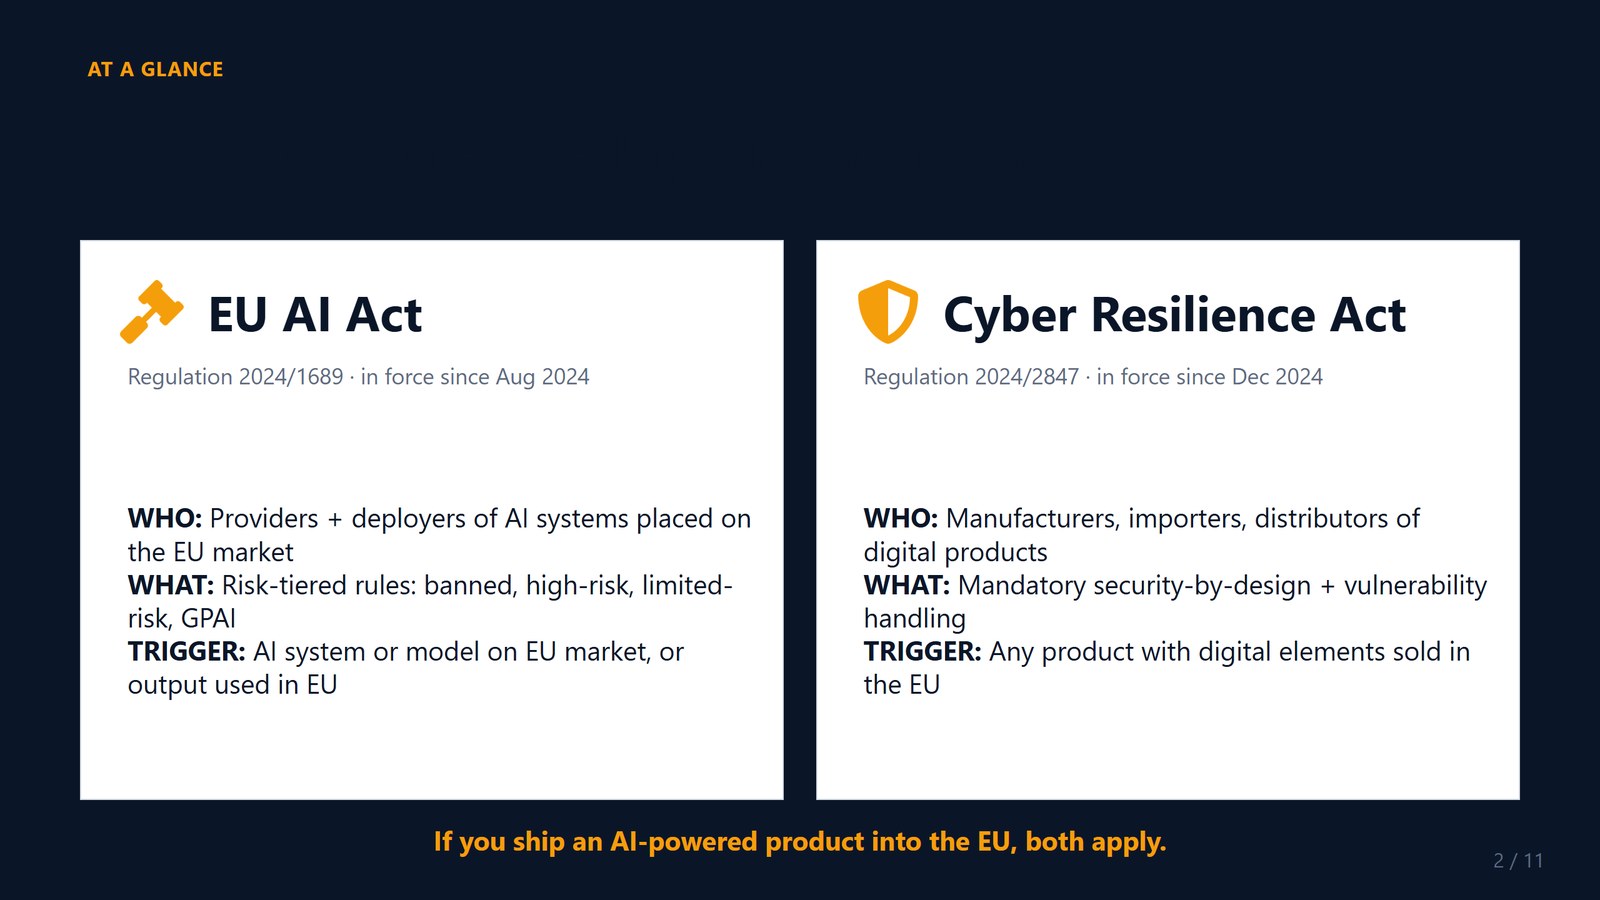
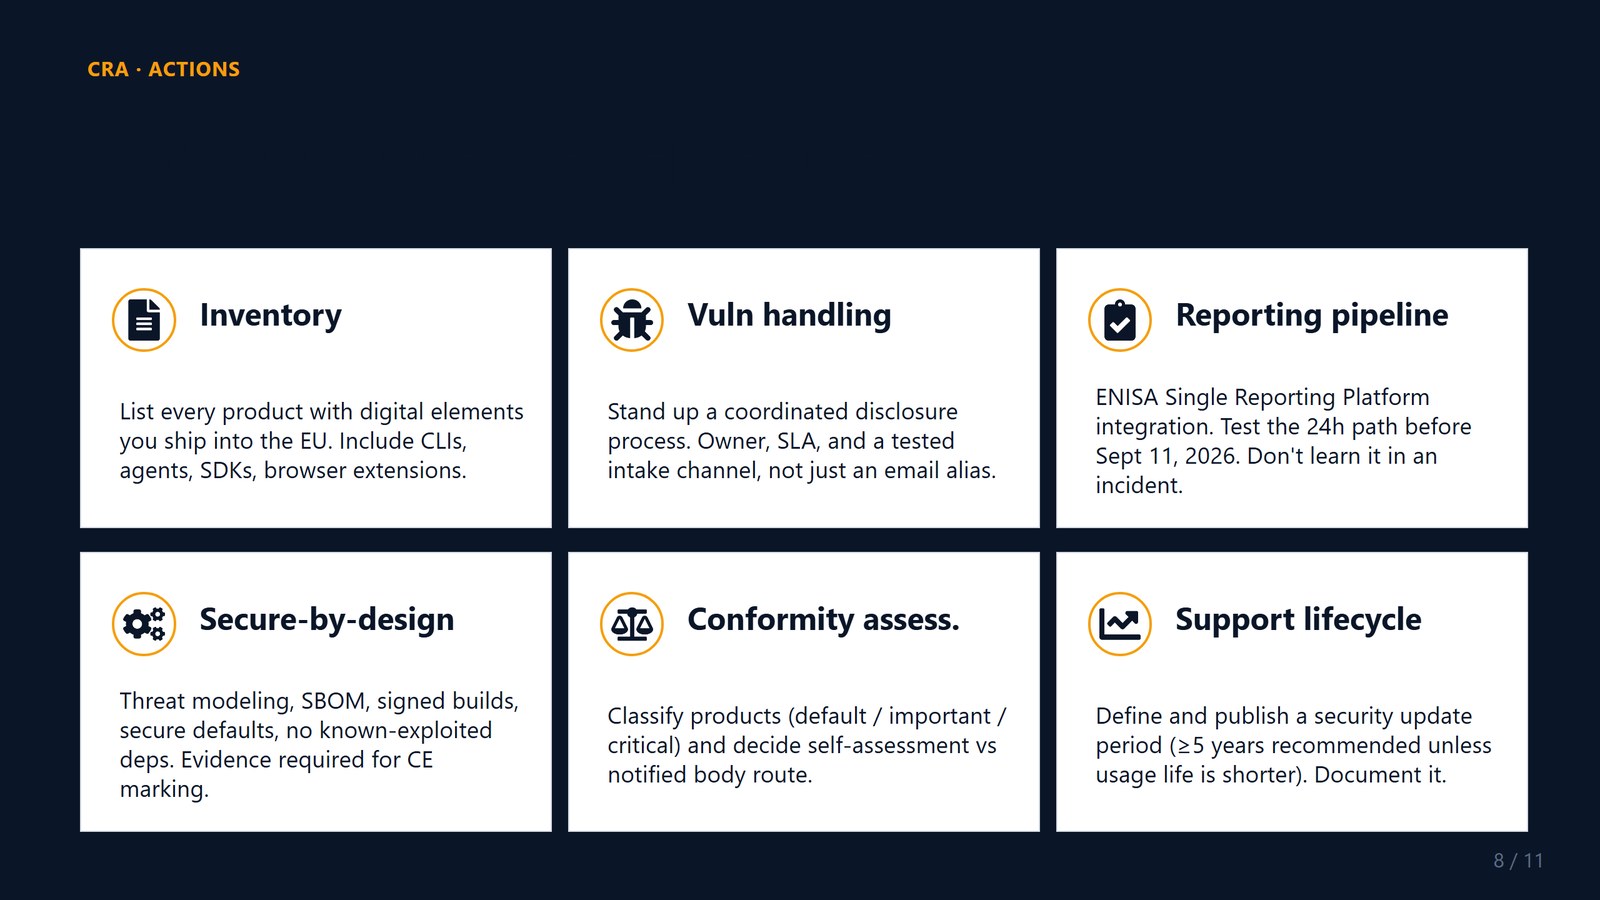
For anyone shipping AI in a product into the EU, both acts apply. They were written by different parts of the Commission with different vocabularies, but the engineering work overlaps heavily. Threat modelling, logging, incident response, technical documentation, post-market monitoring — all show up in both.
The thesis is simple: treat the AI Act and CRA as one engineering problem, not two compliance projects. Build the controls once and map the evidence into both audits. Teams that do this work in the next 90 days will be in a far better position than those who don’t.
The brief, in full
The eleven-slide version — timelines, role-split actions, the 24/72/14 cadence, and the AI Act × CRA overlap map:
Where is your team positioned for the upcoming regulatory deadlines, and how are you preparing?