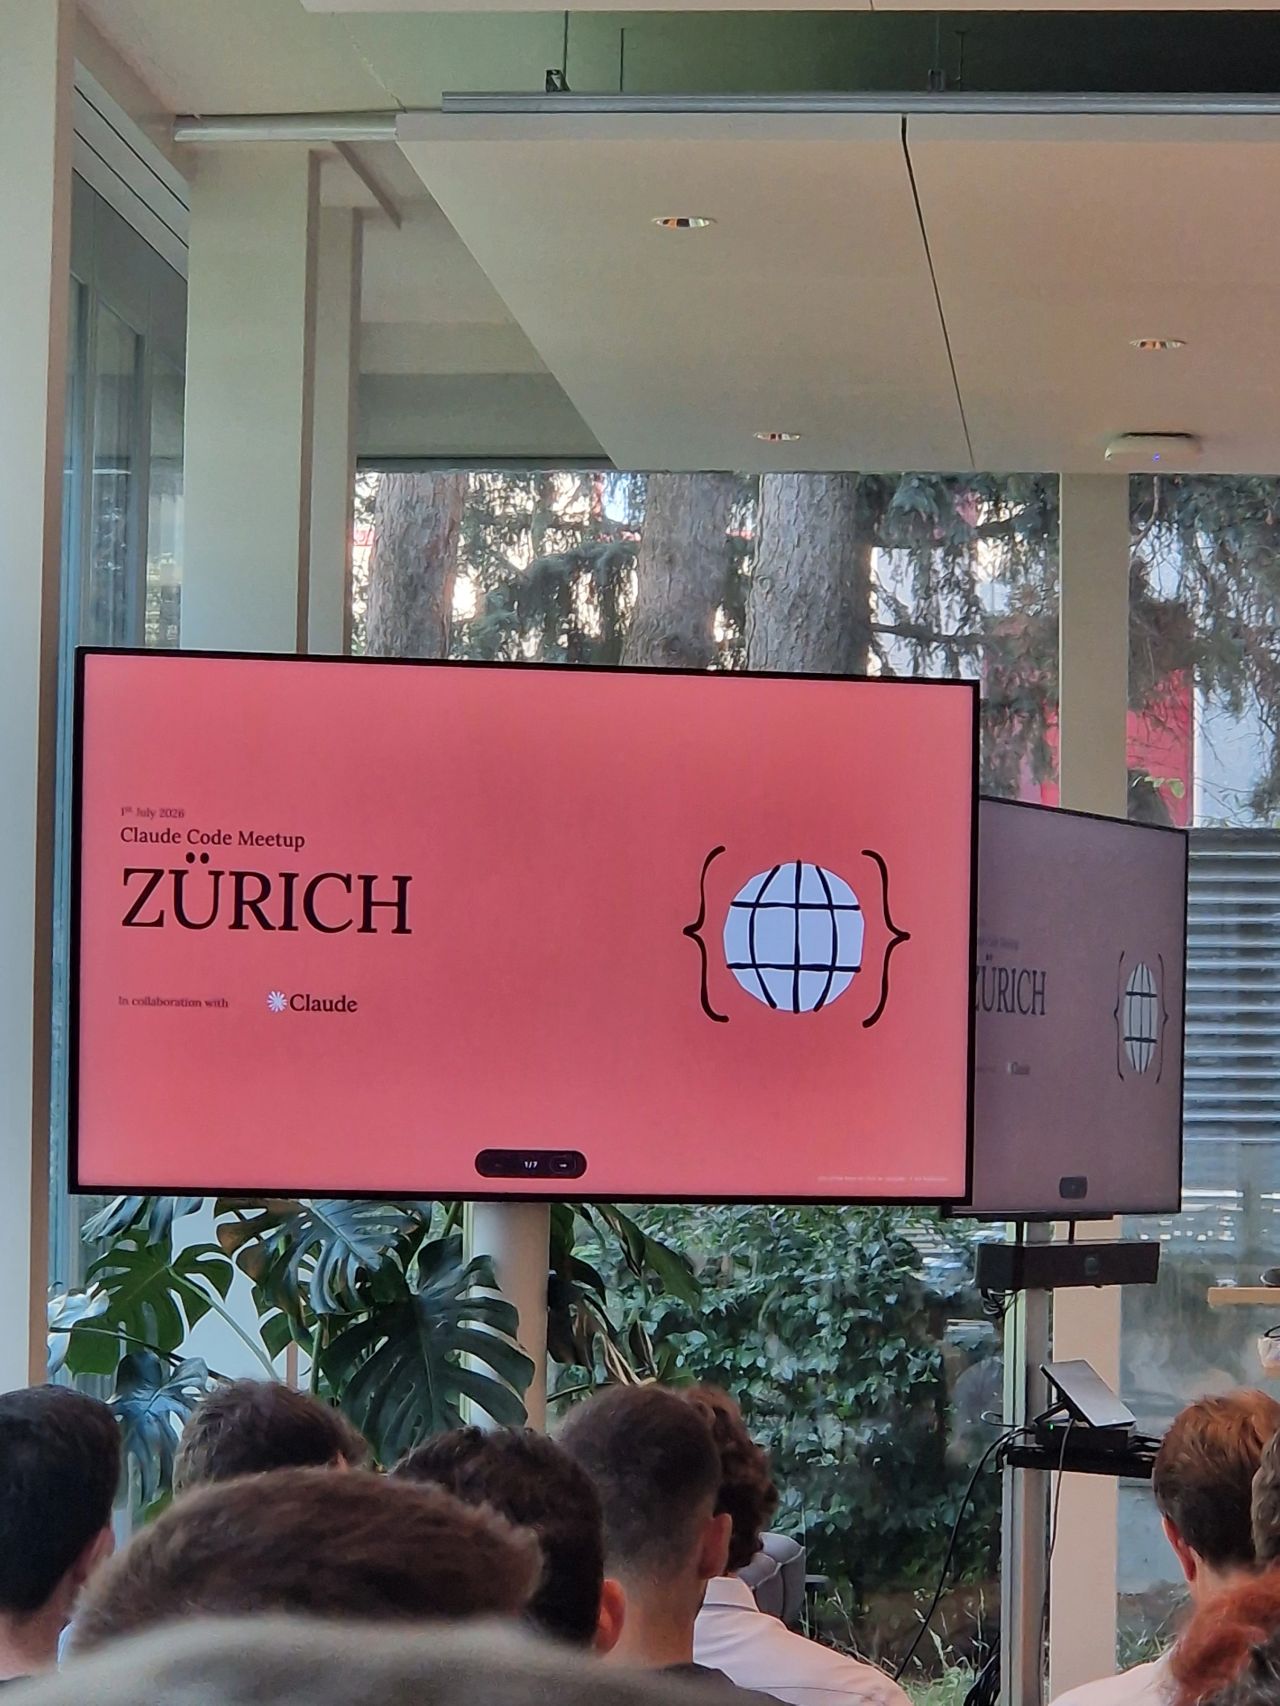
This evening I attended Anthropic’s Claude Code Zürich #2, hosted and organised by Arnaud Delacour, for Claude Code in Regulated Industries.
Adnovum (Daniel Hogg, Ph.D. and Ricardo S) walked through application of Claude Code from greenfield development to refactoring legacy monoliths, with an honest account of how far to trust it at each stage. The part that stayed with me was their approach to building deterministic results out of LLMs by grounding them in reliable data.
Daniel Roman from Google followed with defence in depth at scale, and the data sovereignty that GCP — and Claude by extension — can facilitate in Europe, and the tiers of public / semi-public / private cloud architectures Google offers. Very insightful even as a long-time GCP user.
Bug Bounty Switzerland (Lukas Heppler and Florian Badertscher) discussed the signal-to-noise problem every one of us in security is experiencing, and how they are engineering systems to hold up when AI surfaces findings faster than anyone can triage them.
Overall, a strong evening. As an exclusive event with hundreds on the waitlist, the calibre of people in one room — and what came out of putting them there — was very valuable.
I left considering how a nondeterministic tool earns its place in environments where compliance, and consistent, auditable output, is a hard requirement.
The consensus seems to be traditional deterministic validation, and continuous optimisation of harness and loop engineering around compliance requirements.
Thanks to all who organised and presented — looking forward to more Zürich Claude Code events in the future.